ISO 42001 and the EU AI Act: How They Work Together
Responsible AI Governance
Artificial intelligence is becoming a critical part of modern business systems. For organisations operating in the UK and EU, two frameworks are becoming increasingly important: ISO/IEC 42001 and the EU AI Act. Although they serve different purposes, they are closely related — and many organisations are implementing ISO 42001 as a practical way to prepare for the governance expectations introduced by the EU AI Act.
What Is the EU AI Act?
The EU Artificial Intelligence Act is the first comprehensive regulatory framework designed to govern the use of artificial intelligence in the European Union. The legislation introduces a risk-based approach to AI regulation, meaning that obligations increase depending on the level of risk posed by an AI system.
In practice, this means organisations must first identify whether their AI systems fall into regulated categories and then implement appropriate controls such as documentation, risk assessments, and monitoring processes. The Act broadly categorises AI systems into four levels:
| Risk Level | Description |
|---|---|
| Unacceptable risk | AI systems that are prohibited |
| High risk | AI systems subject to strict regulatory requirements |
| Limited risk | AI systems requiring transparency obligations |
| Minimal risk | AI systems with limited regulatory requirements |
High-risk AI systems may include technologies used in areas such as:
- recruitment and employment decisions
- credit scoring and financial services
- healthcare diagnostics
- biometric identification
- critical infrastructure management
Organisations deploying these systems must implement governance processes to ensure that risks are identified and managed appropriately, such as documenting how the AI system works, performing risk assessments before deployment, monitoring performance after release, and ensuring humans can intervene when necessary.
What Is ISO 42001?
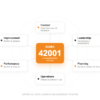
ISO/IEC 42001 is an international standard that provides requirements for establishing and operating an Artificial Intelligence Management System (AIMS). The standard helps organisations implement governance processes that ensure AI systems are:
- properly documented
- monitored for performance and reliability
- assessed for risks such as bias or misuse
- subject to appropriate oversight and accountability
These requirements are implemented through an Artificial Intelligence Management System (AIMS), similar in structure to management systems used in standards like ISO 27001 or ISO 9001. In practice, this means organisations define policies, assign responsibilities, document AI systems in use, and regularly review whether those systems are operating safely and as intended.
Unlike the EU AI Act, ISO 42001 is not a law. Instead, it provides a structured management system framework for responsible AI governance.
Key Difference Between ISO 42001 and the EU AI Act
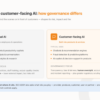
The two frameworks have different roles.
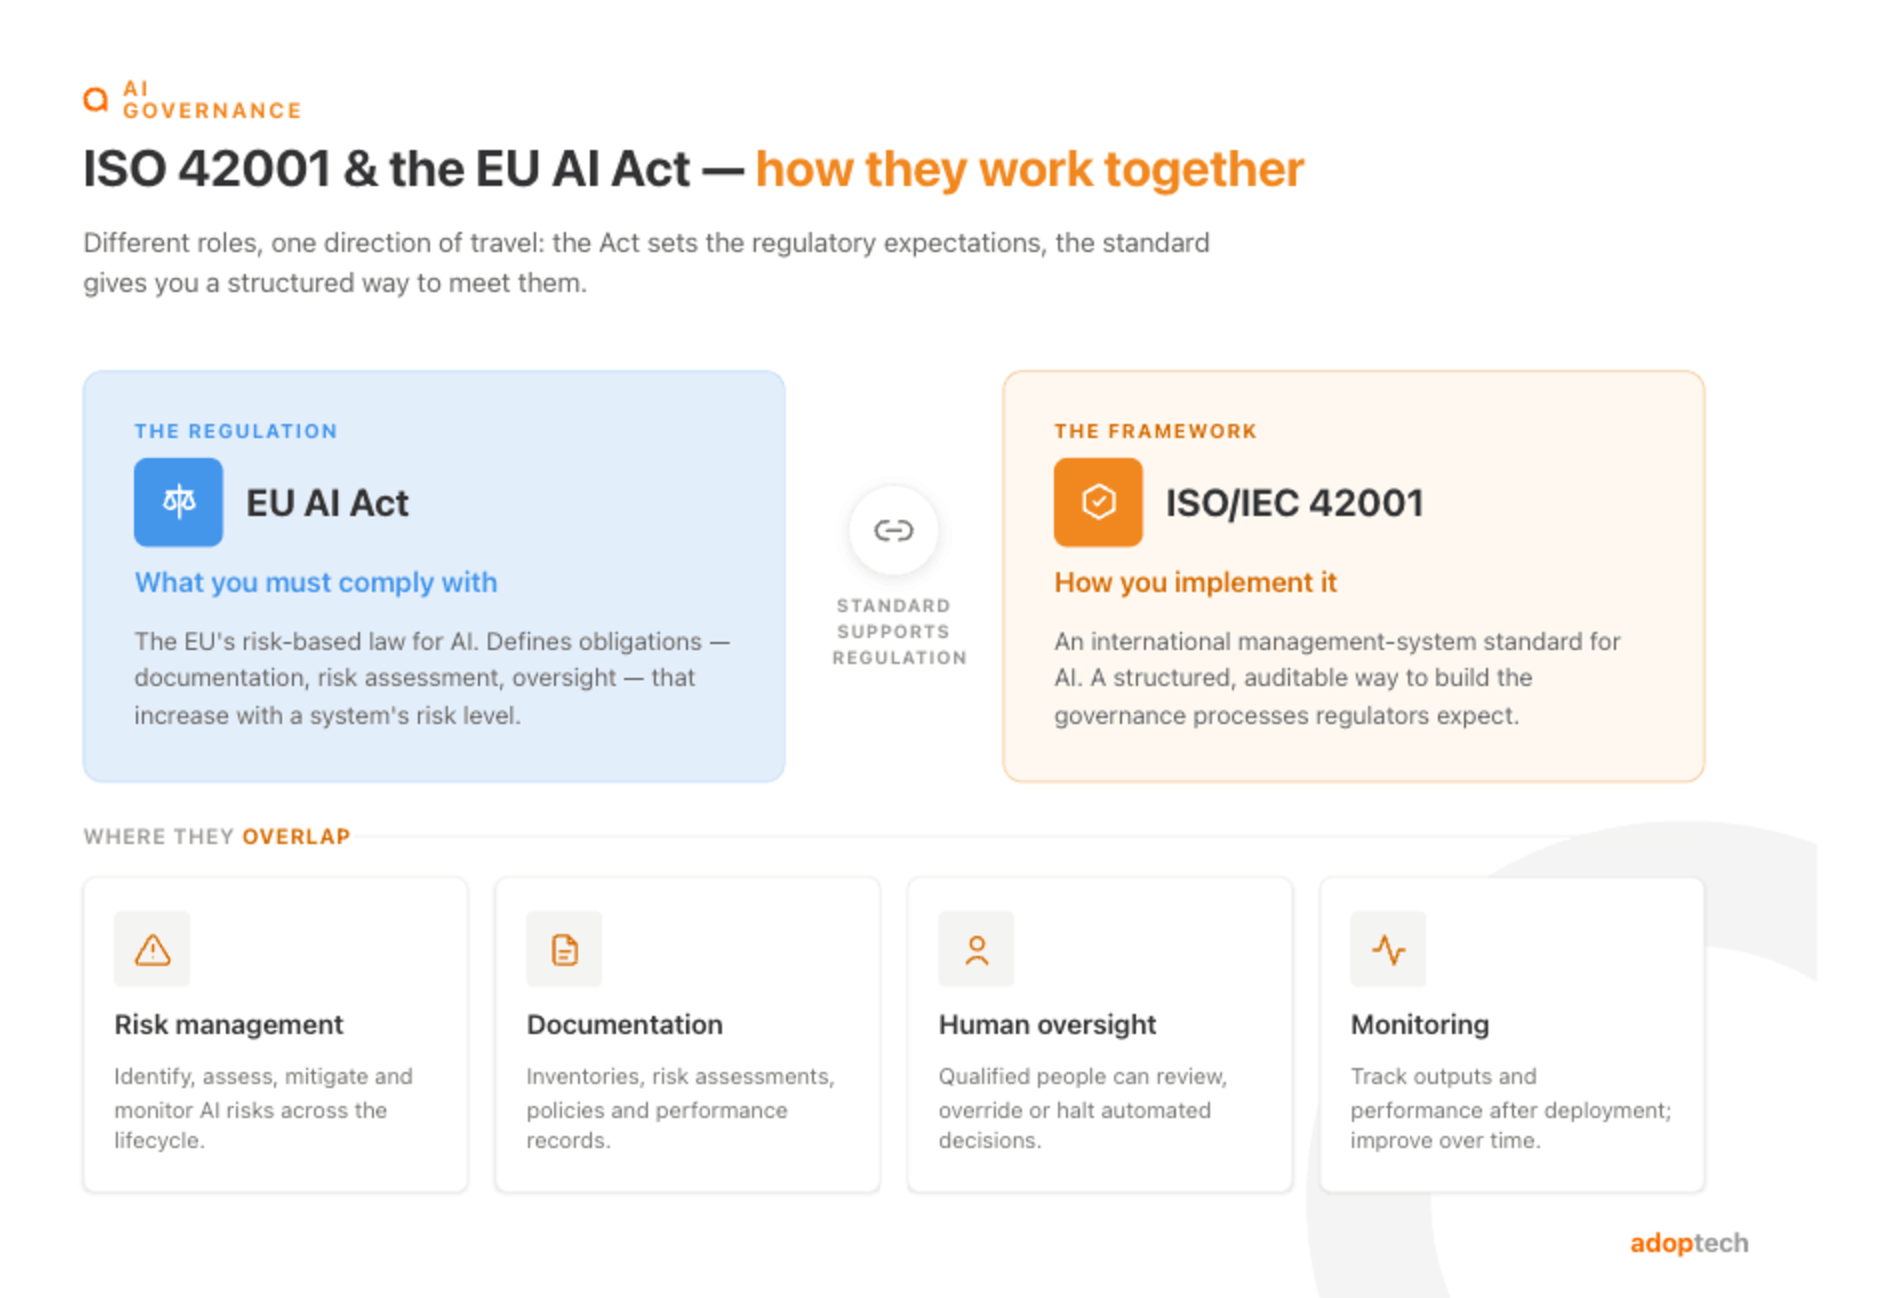
EU AI Act
Legal regulation governing certain AI systems. Defines what organisations must comply with and sets regulatory expectations.
ISO 42001
Management system standard for AI governance. Provides a structured framework organisations can use to build internal processes to meet those expectations.
In practice, many organisations use ISO 42001 to help structure their approach to AI risk management in a way that aligns with what regulators expect.
How ISO 42001 Supports EU AI Act Compliance
Although ISO 42001 does not replace the EU AI Act, it helps organisations implement many of the governance processes that regulators expect. Several areas of overlap include the following.
Why Many European Organisations Are Adopting ISO 42001
As AI adoption increases, organisations are recognising that informal or ad-hoc governance approaches are often insufficient to manage regulatory and operational risks. For organisations operating in Europe, ISO 42001 provides a structured way to implement AI governance practices aligned with regulatory expectations.
Will ISO 42001 Become Important for EU AI Act Compliance?
ISO 42001 is not formally required by the EU AI Act. However, international standards are often used by regulators and organisations as practical frameworks for implementing governance requirements.
Many organisations therefore view ISO 42001 as a useful foundation for building the governance processes needed to comply with evolving AI regulations in Europe. By implementing ISO 42001, organisations can establish structured processes for risk management, documentation, and oversight that regulators increasingly expect when assessing AI systems.
Key Takeaways
The EU AI Act and ISO 42001 serve complementary roles in the governance of artificial intelligence.
- The EU AI Act establishes regulatory requirements for certain AI systems
- ISO 42001 provides a management system framework that helps organisations implement structured AI governance
For organisations operating in the UK and European Union, adopting ISO 42001 can help create the governance processes needed to manage AI responsibly and prepare for regulatory expectations. Organisations that begin implementing structured AI governance early may find it easier to adapt as regulatory expectations around AI continue to evolve.
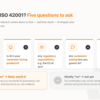
Frequently Asked Questions
No. ISO 42001 is not a regulatory requirement and does not automatically guarantee compliance with the EU AI Act. However, the governance processes implemented through ISO 42001 may support preparation for regulatory obligations.
No. The EU AI Act does not require organisations to implement ISO 42001. It is a voluntary standard.
Many European organisations are adopting ISO 42001 because it provides a structured framework for AI governance that aligns with emerging regulatory expectations.
Yes. Organisations implementing ISO 42001 can demonstrate that they have formal governance processes for managing AI risks, monitoring AI systems, and maintaining accountability.
Preparing for the EU AI Act?
Adoptech helps organisations implement ISO 42001 and build the AI governance processes needed to meet evolving regulatory expectations — with expert UK-based support throughout.